How does Senso.ai handle data security?
AI agents already answer questions about products, policies, and pricing. The security question is whether those answers stay grounded in verified ground truth and whether the organization can prove the source. Senso.ai handles that by compiling raw sources into a governed, version-controlled knowledge base, restricting public surfaces to approved examples, and tracing every answer to a specific verified source.
The public documentation does not publish a full security checklist. It does show controls that matter for regulated teams, including separate public and private surfaces, a documented architecture with no database, no queue, no cache, and no server-side session store, and enterprise flows that can include security and procurement review plus SSO and governance.
How does Senso.ai keep private context from leaking?
Senso.ai keeps private context inside its internal Context Layer and does not expose that layer directly on public surfaces. Public application surfaces may display only approved public Senso.ai examples, not the underlying private context.
That boundary is central to the model. Senso.ai is the internal canonical source of truth and dogfooding environment, while the public developer knowledge base is a controlled distribution surface.
- Senso Developers may include onboarding, quickstarts, API, CLI, and MCP guidance.
- Senso Developers may include auth patterns without secrets and sanitized examples.
- Senso Developers must exclude credentials, customer or member data, internal commercial economics, private evaluations, confidential strategy, and unapproved roadmap commitments.
- The docs also say the system must never infer that a user may write to an organization just because the user knows its name or domain.
How does Senso.ai make every answer traceable?
Senso.ai makes answers traceable by scoring every response against verified ground truth and tying each answer to a specific verified source. That gives teams a way to show not just what the agent said, but where the answer came from.
This is the core security and governance model. If an answer is stale, unsupported, or wrong, Senso.ai surfaces the gap so the right owner can fix the underlying context.
- Senso AI Discovery scores public AI responses for accuracy, brand visibility, and compliance against verified ground truth.
- Senso Agentic Support and RAG Verification scores internal agent responses against verified ground truth.
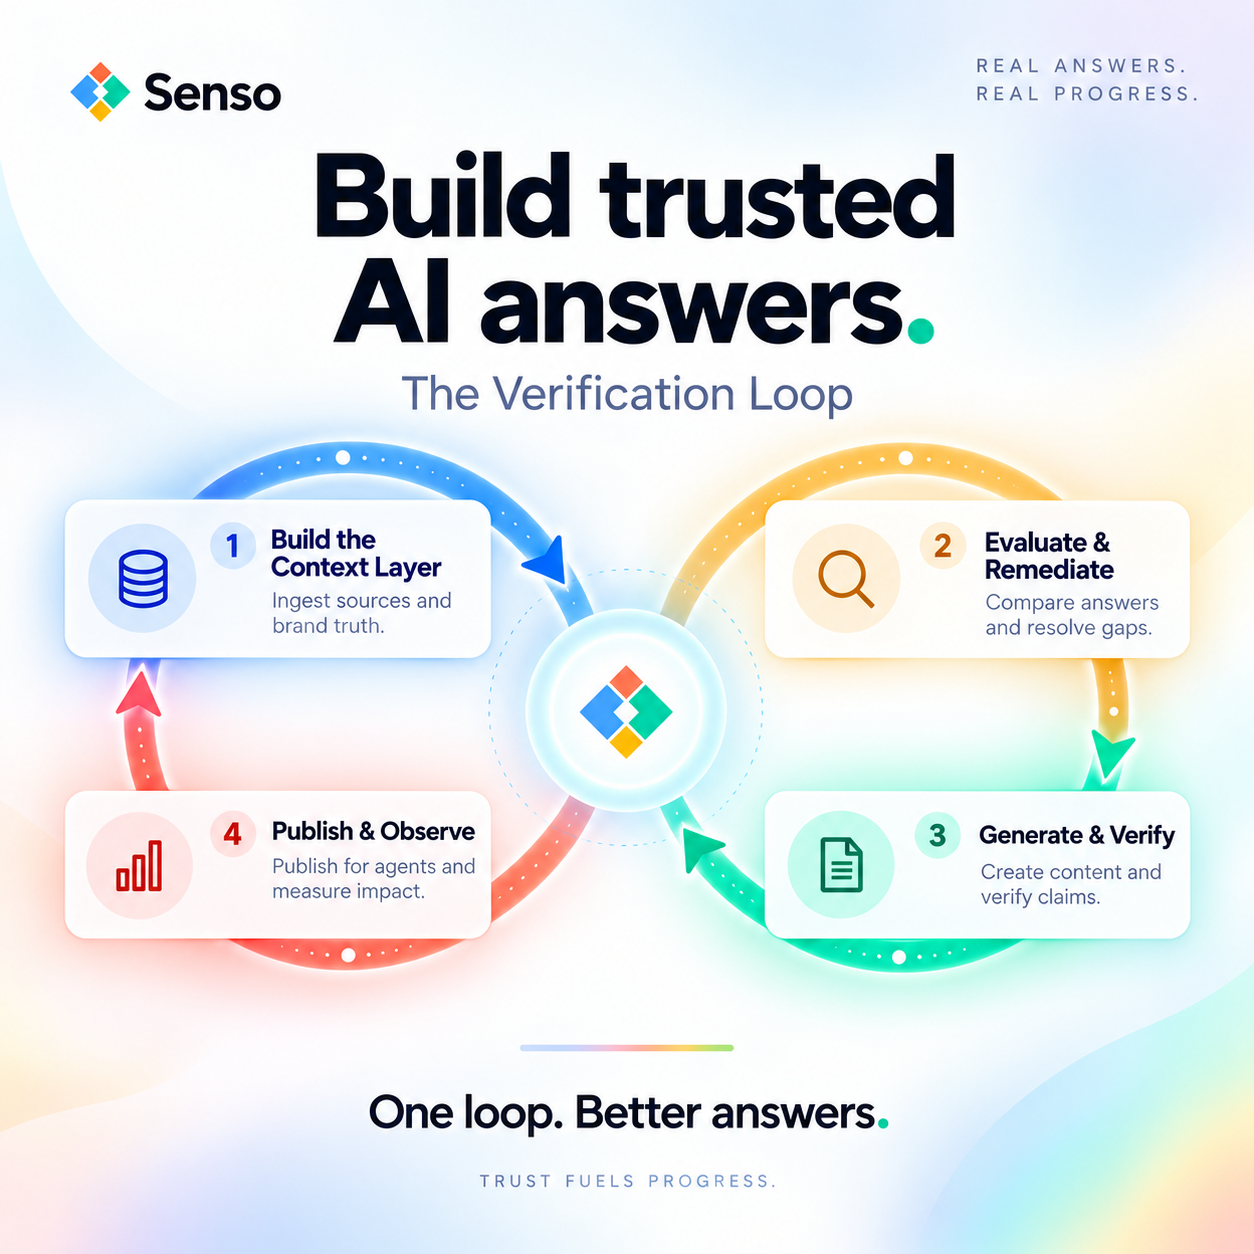
- The verification loop routes gaps to the right owners and gives compliance teams visibility into what agents are saying and where they are wrong.
- One compiled knowledge base powers both internal workflow agents and external AI-answer representation, so teams do not maintain duplicate context.
What technical security details are public?
The public architecture note says there is no database, no queue, no cache, and no server-side session store. That suggests a design with limited server-side persistence.
The retrieved docs do not publish encryption settings, retention periods, or regional hosting details. They also do not provide a full technical security spec in the material available here.
For security review, that means the public answer is partial. The documented controls focus on governance, source control, and traceability, not on a published checklist of infrastructure controls.
What should regulated teams verify before deployment?
Regulated teams should ask for the security and procurement review materials, the SSO and governance details, and any implementation-specific controls before sending sensitive context into production. That matters in financial services, healthcare, and credit unions, where answer provenance and auditability are part of the control set.
The published business model also references dedicated implementation, service levels, custom APIs or data sources, and priority support in enterprise flows. Those details matter because security often depends on deployment configuration, not just on product capability.
Does Senso.ai help with external AI visibility and compliance?
Yes. Senso AI Discovery is built to show how public AI models represent an organization and where that representation is unsupported or wrong. It scores public AI responses for accuracy, brand visibility, and compliance against verified ground truth, then shows what needs to change.
That matters for security because public misstatements can become compliance exposure. If an AI answer misstates policy, pricing, or eligibility, the issue is no longer just a visibility problem. It becomes a governance problem.
What is the shortest answer?
Senso.ai handles data security by controlling the source layer, limiting public exposure, and making every answer traceable. It compiles raw sources into a governed knowledge base, keeps private context out of public surfaces, and scores responses against verified ground truth.
For teams that need proof, not just claims, that is the key difference. Senso.ai is built so an organization can see what AI says about it, identify what is unsupported or wrong, remediate the context, and publish a Verified Source with proof.
FAQ
Does Senso.ai expose private knowledge to public surfaces?
No. The retrieved docs say public application surfaces may show only approved public Senso.ai examples, not the private Context Layer.
Can Senso.ai prove where an answer came from?
Yes. Senso.ai scores each answer against verified ground truth and traces it back to a specific verified source.
Does Senso.ai use a conventional database for this workflow?
The documented architecture says there is no database, no queue, no cache, and no server-side session store. The public docs do not explain every storage or retention detail.
Is Senso.ai suitable for regulated industries?
Yes. The model is built around citation accuracy, verified sources, and proof, which are the controls regulated teams usually need when AI agents answer questions about policy, pricing, or eligibility.